Authentication
All Partner API calls are authenticated with an API token that belongs to your seller wallet.
Get a token
- Log in to the seller dashboard (admin.sevi.io for production; we give you access to the staging dashboard for the sandbox).
- Open Settings.
- Click Generate to create an API token. To replace a token, revoke the current one first and generate a new one.
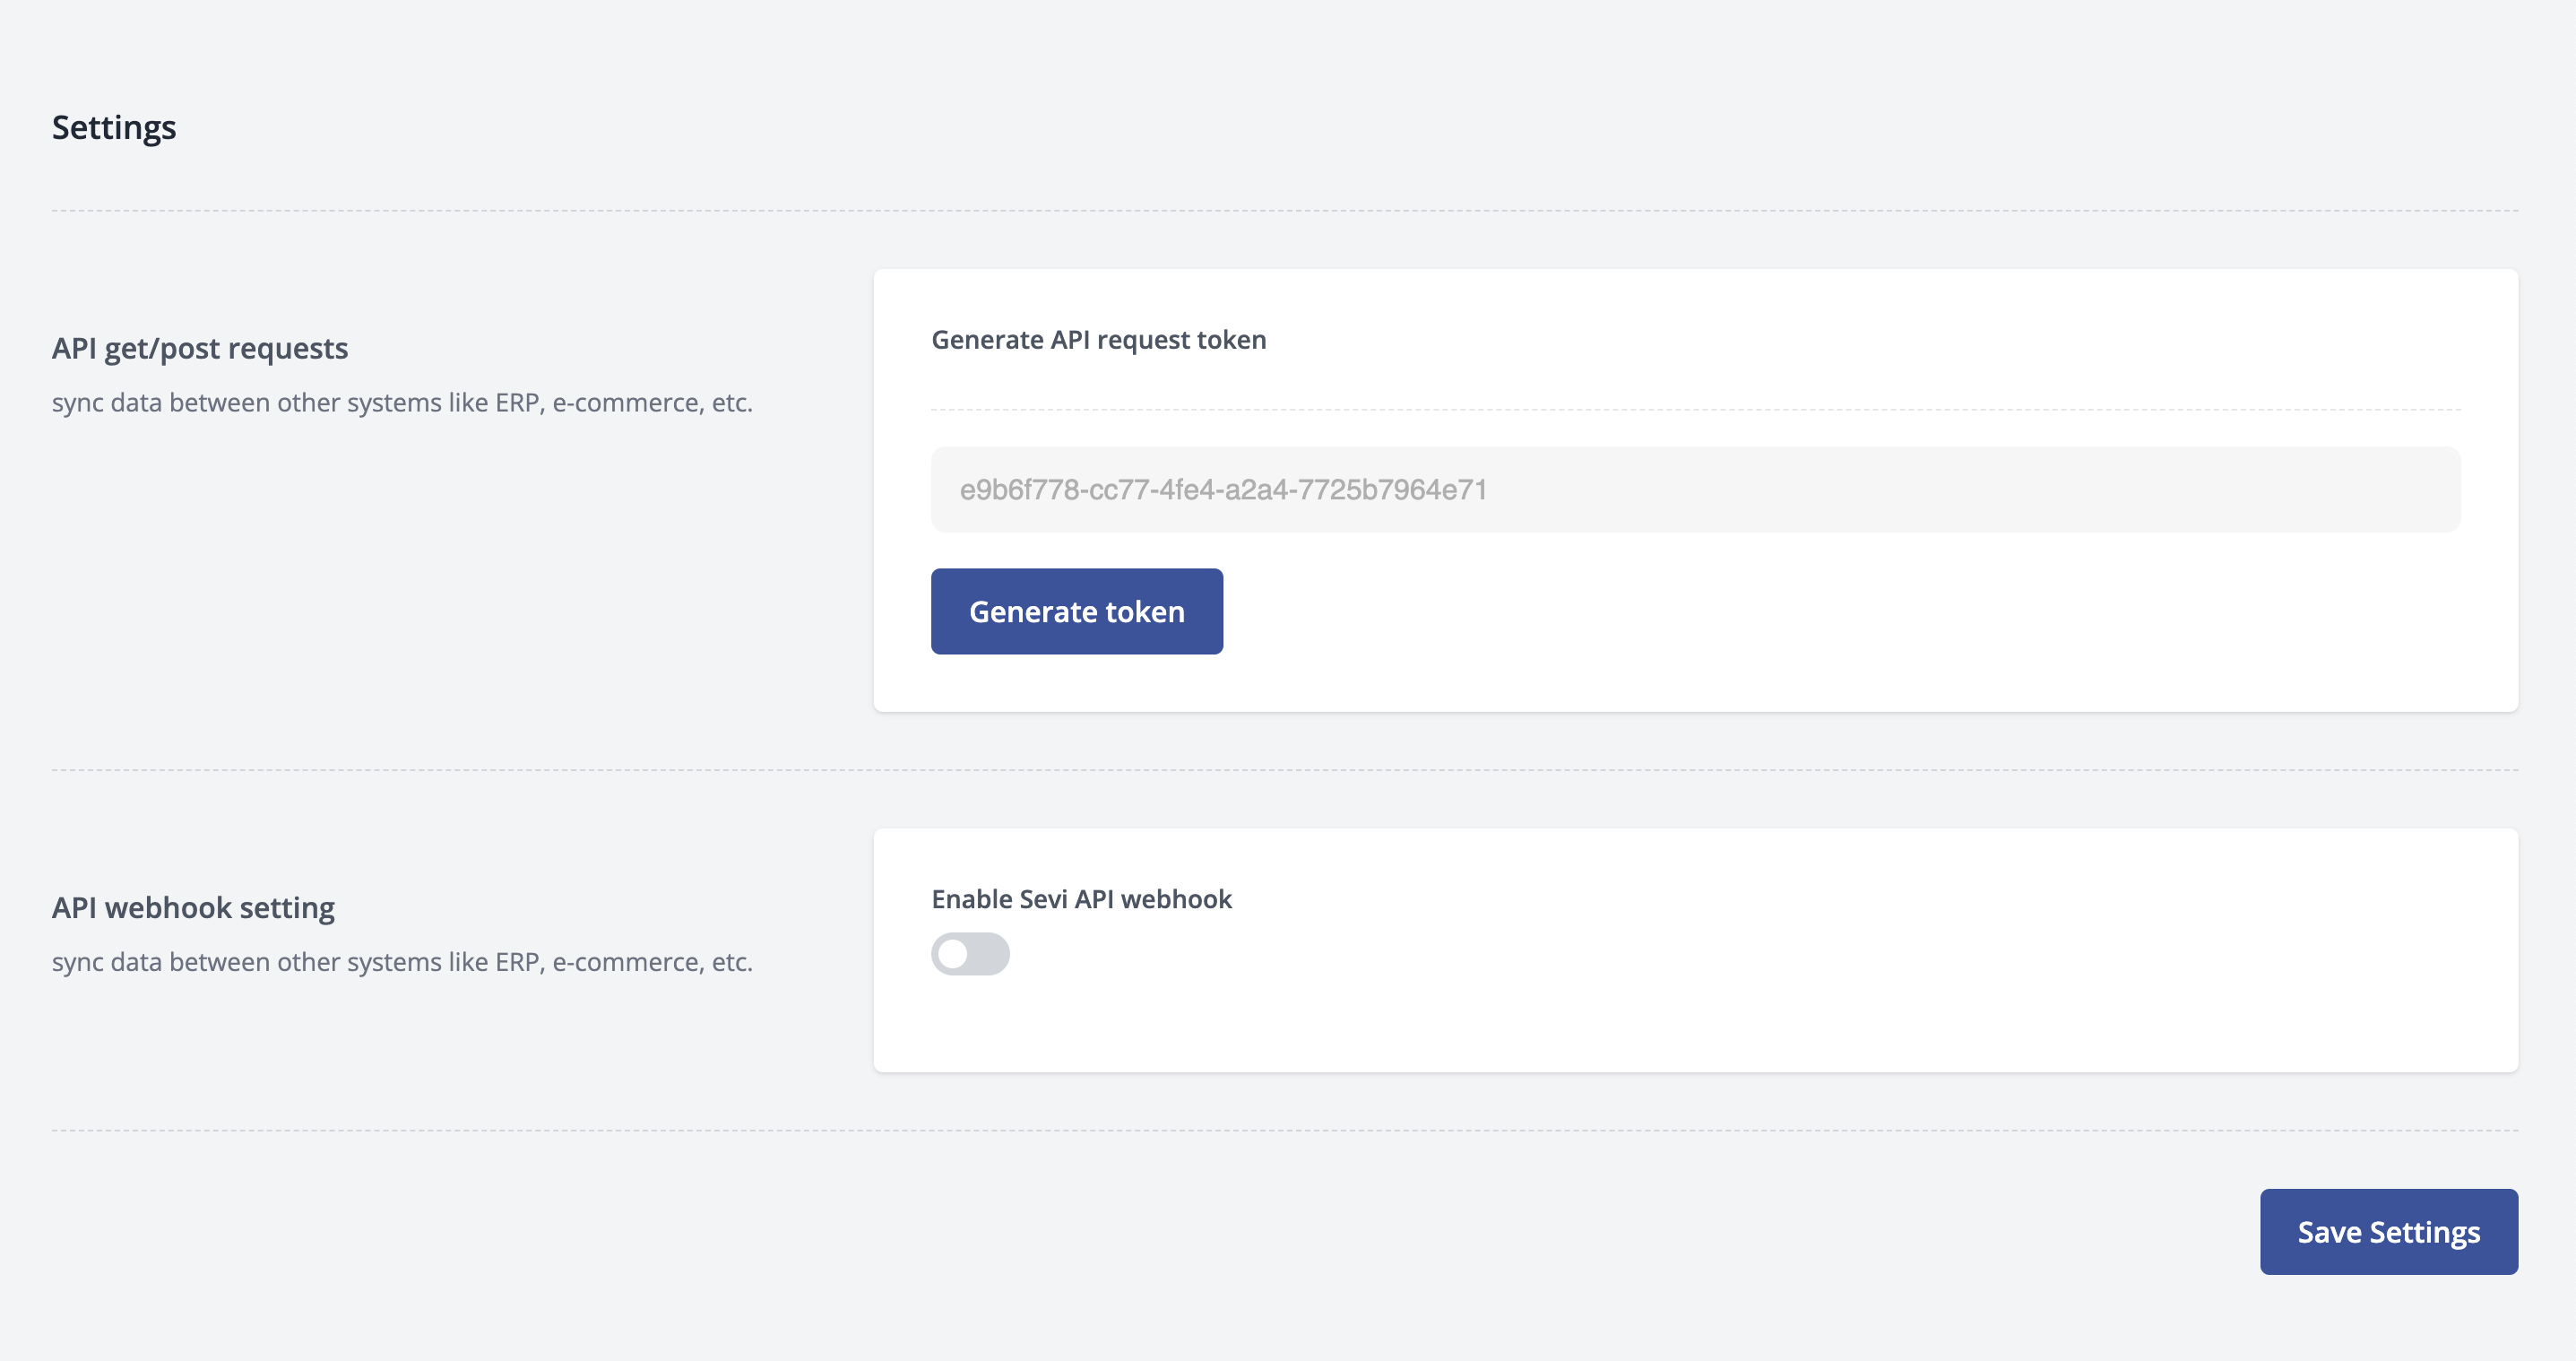
Sandbox and production tokens are different — a sandbox token does not work on partner.sevi.io and vice versa.
Use the token
Send the token verbatim in the Authorization header of every request (no Bearer prefix):
curl https://sandbox.sevi.io/graphql \
  -H 'Content-Type: application/json' \
  -H 'Authorization: <your API token>' \
  -d '{"query":"query($input: OrderSearchInput!){ orderSearch(input:$input){ order { id status paymentStatus } } }","variables":{"input":{"referenceNumber":"D123456"}}}'
Keep it secret
The token gives full programmatic access to your seller account. Keep it on your server only — never in a mobile app, browser code or source control. If it leaks, revoke it in the dashboard and generate a new one.
The API token is not the same as the webhook token: the webhook token is what Sevi sends to you so you can verify incoming webhooks — see Webhook authorization.